A Two-Layer Personal-Agent Workflow Using Grok Bot and Cursor
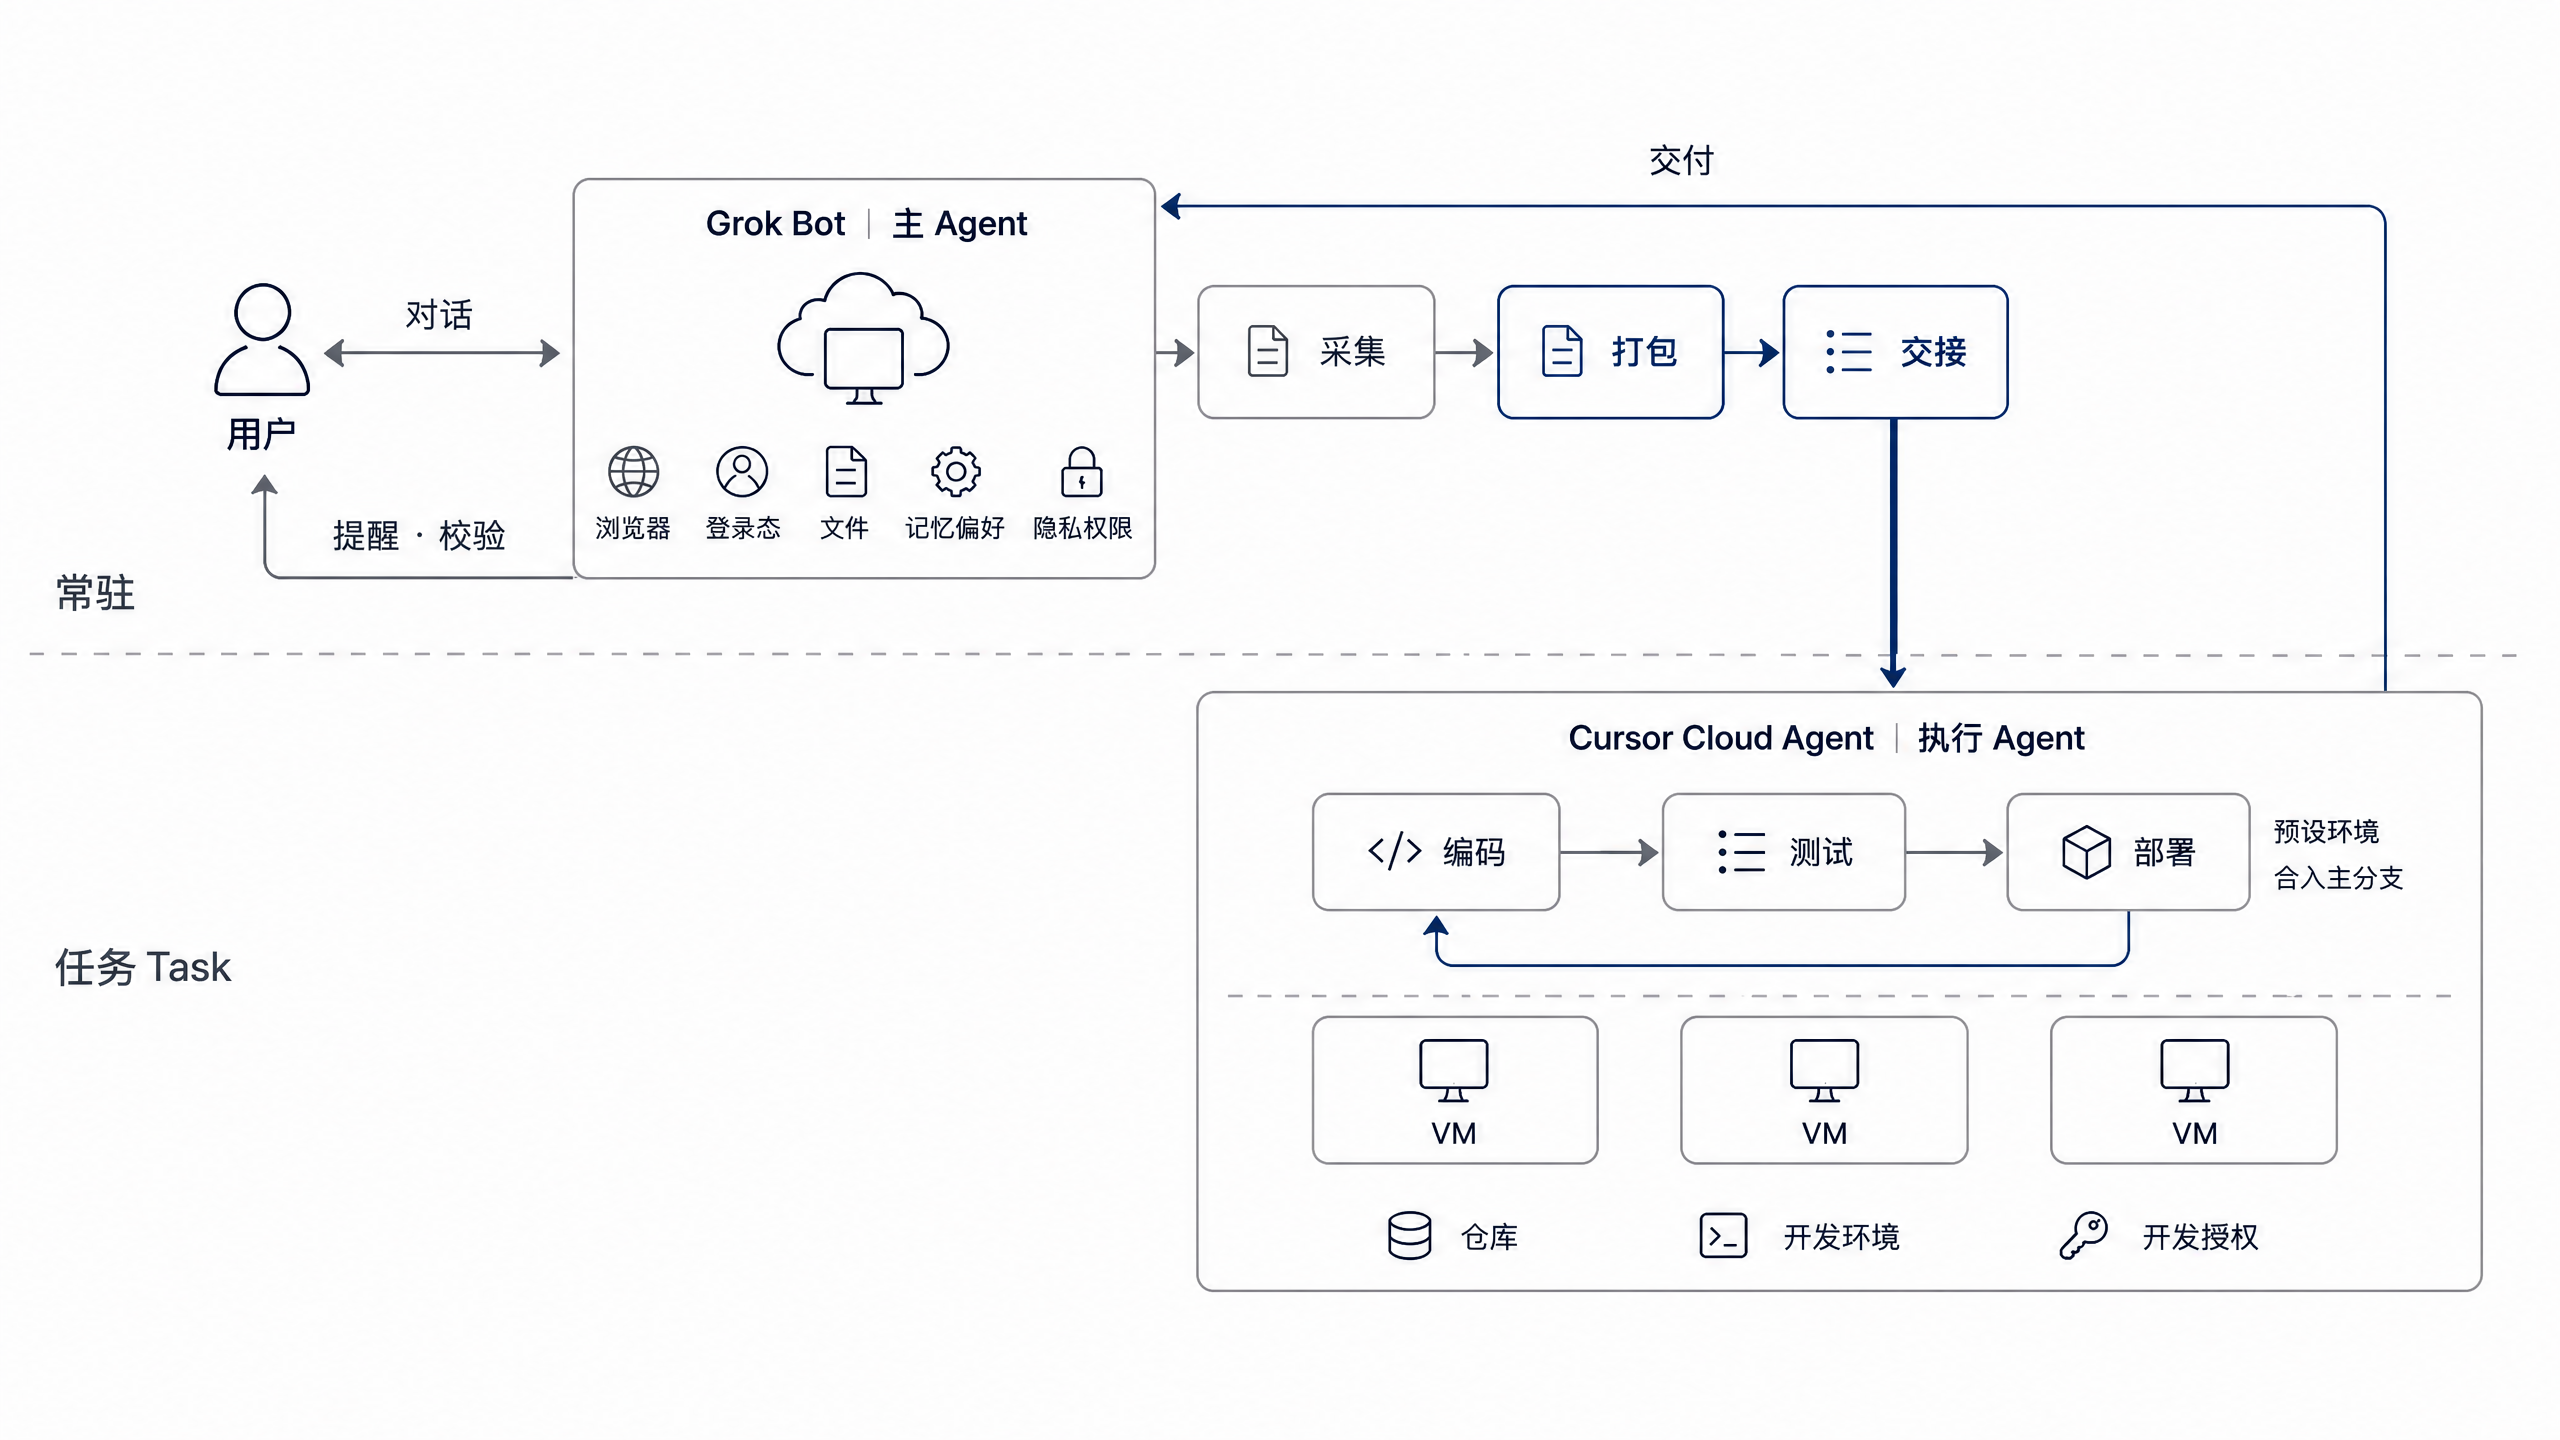
An author proposes dividing a personal agent into a persistent identity layer and a task-specific execution layer. In the proposed workflow, Grok Bot would run on a persistent cloud computer, retain login state, files, preferences and cross-task memory, and hold privacy-related permissions. Cursor Cloud Agent would execute coding, testing and deployment in a separate virtual machine for each task, then return a preview or production link to Grok Bot for user validation. The author describes this as the result of personal experimentation and remains unsure how Grok Bot should work with an existing Cursor local-and-cloud setup.
前言:https://web.okjike.com/u/815916E7-5BD5-4EC6-9EB1-14458F0E11CE/post/6af449d0320fd7e1b55f5a0f grokbot 如此独立但也很巧妙 我今天有点搞不明白,如果我已经有 Cursor local+cloud,如何和 grokbot 协作呢? 至少今晚摸索的结果是👇 个人 Agent 按归属分为两层: 身份层随人常驻,执行层随任务分配。 身份层由 Grok Bot 承担,运行在持久云电脑上,保存登录态、文件、偏好与跨任务记忆,持有隐私类权限。 它负责理解意图、定时采集信息,并将原始信息压缩为结构完整的任务交付物。 执行层由 Cursor Cloud Agent 承担,每个任务分配独立的虚拟机,在其中完成编码、测试与部署的全部闭环,最终产出预览链接或正式链接。 链接交回身份层后,Grok Bot 向用户发出提醒并请用户校验。 用户只在任务的起点和终点介入:起点表达意图,终点确认结果。