Claude Code reportedly exposed user email and repository metadata
A 36Kr/New Intelligence report citing reverse-engineering of Claude Code v2.1.220 says the client placed a logged-in user's email in the system prompt, allowing requests to external sites to expose identity details. Commenter-posted server logs also reportedly showed a user's name, team and internal GitHub repository paths in request headers, while Anthropic engineer Lydia Hallie acknowledged the email's presence in context. Anthropic added a default-on email-blocking plugin in v2.1.317, but Hallie said it cannot block requests written by Claude itself, and v2.1.319 was the latest version reported.
The disclosure highlights a privacy risk for coding agents that place account metadata into model context and give models broad network and scripting access.
用户每月掏几十甚至 200 美元订阅 Claude Code,把本地终端交给它干活,它却在后台把你的真实登录邮箱、姓名乃至公司内部代码库地址,塞进 User-Agent 请求头里发给了外部网站!
Anthropic 工程师图省事,偷偷把登录邮箱硬编码进每次对话的系统提示词,而 Claude,一遇到要求登记联系方式的网站,就顺手从提示词里取出真邮箱发了出去。
图省事,出卖了用户隐私
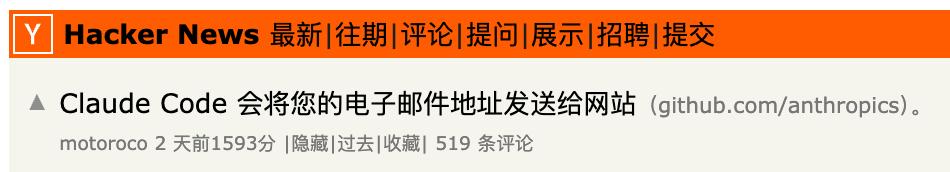
2026 年 11 月 5 日,Hacker News 上一条控诉 Claude Code 外发用户邮箱的帖子迅速冲上了热门。
发帖人每天收到几十封直呼真名的诈骗邮件,发信域名他一个也没访问过。
#Anthropic#Claude Code#Claude Opus 5.5#GitHub#U.S. Securities and Exchange Commission